Account takeover field guides
Explore credential stuffing, passwordless sessions, identity exposure, impossible travel, trusted integration, recovery and customer impact.
Practical reading for the teams connecting identity, product, engineering, fraud operations and support.
Latest guides
How to prevent account takeover across the access journey
Build an account takeover prevention plan across authentication, device and network risk, sensitive actions, session containment and protected recovery.
Detect credential stuffing behind residential proxies
Detect distributed credential stuffing with account, device and network evidence. Evaluate low-rate attempts, valid logins and legitimate shared-network users.
Account takeover risk in passwordless login and sessions
Understand what passkeys protect, where session and recovery risk remains, and how to evaluate account controls around a passwordless login journey.
Credential exposure monitoring before account takeover
Compare compromised-credential and session-artifact monitoring with live login risk. Plan identity matching, remediation and verification without collecting raw secrets.
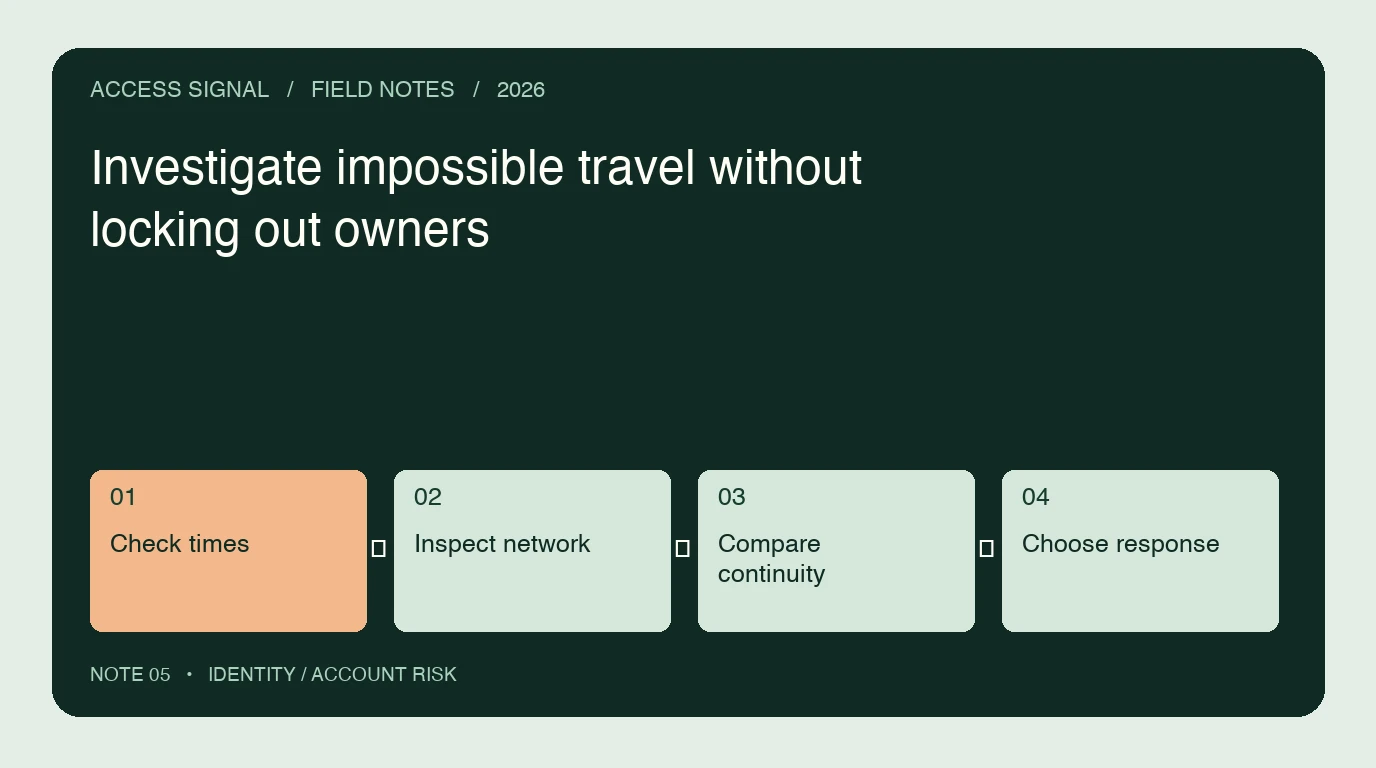
Investigate impossible travel without locking out owners
Investigate impossible-travel alerts with device continuity, network context, timestamps and session actions. Separate IP geolocation changes from confirmed compromise.
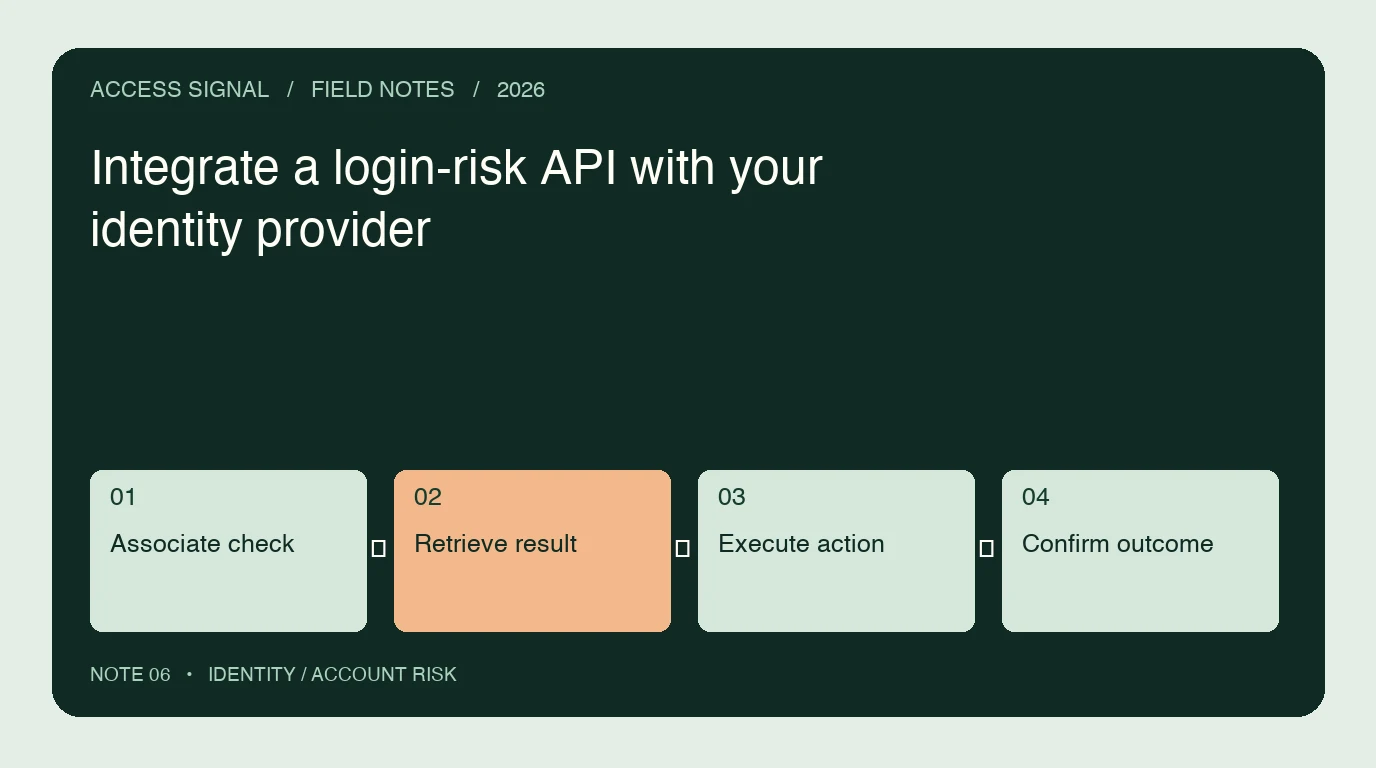
Integrate a login-risk API with your identity provider
Build trusted login-risk integration around account and action references, server-side results, freshness, step-up confirmation, timeouts and session controls.
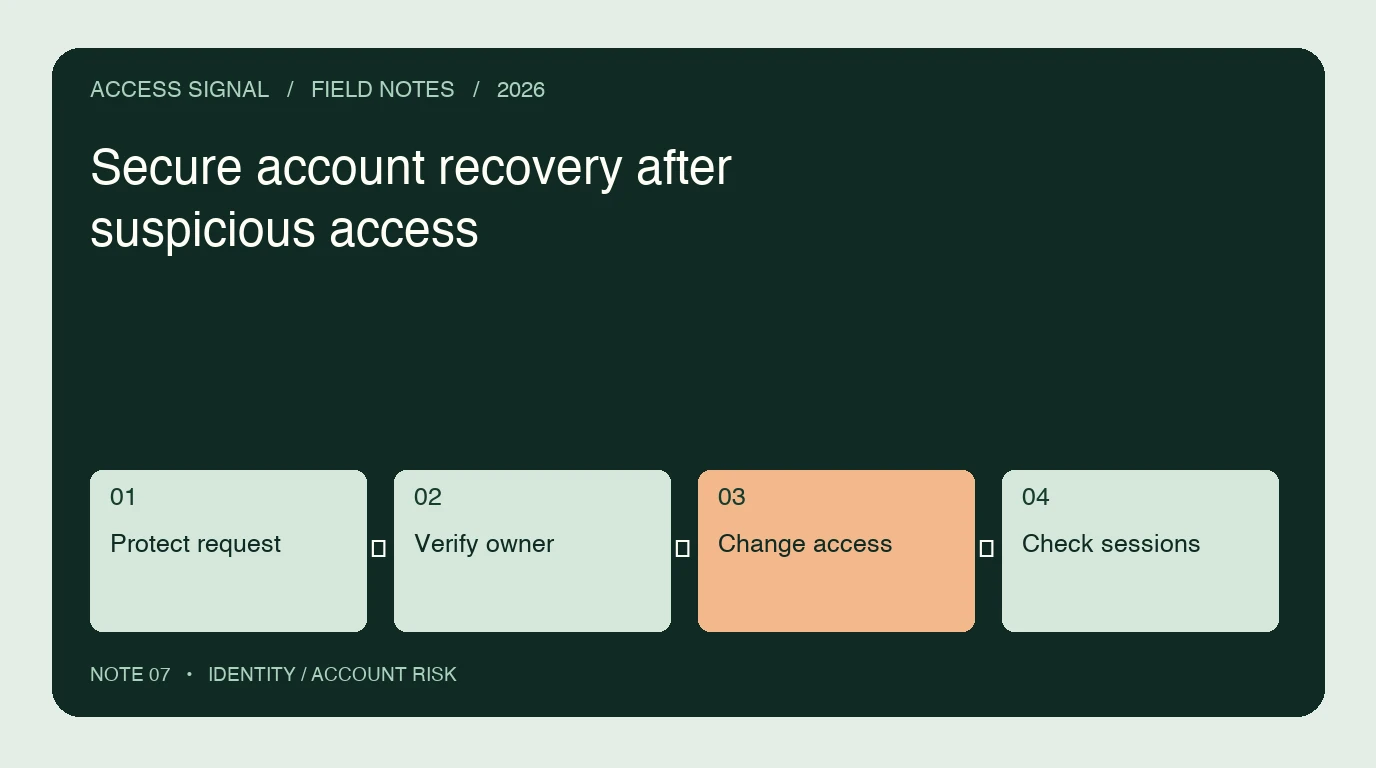
Secure account recovery after suspicious access
Protect account recovery with safe reset handling, proportionate device-risk checks, owner verification and confirmed session consequences after a reset.
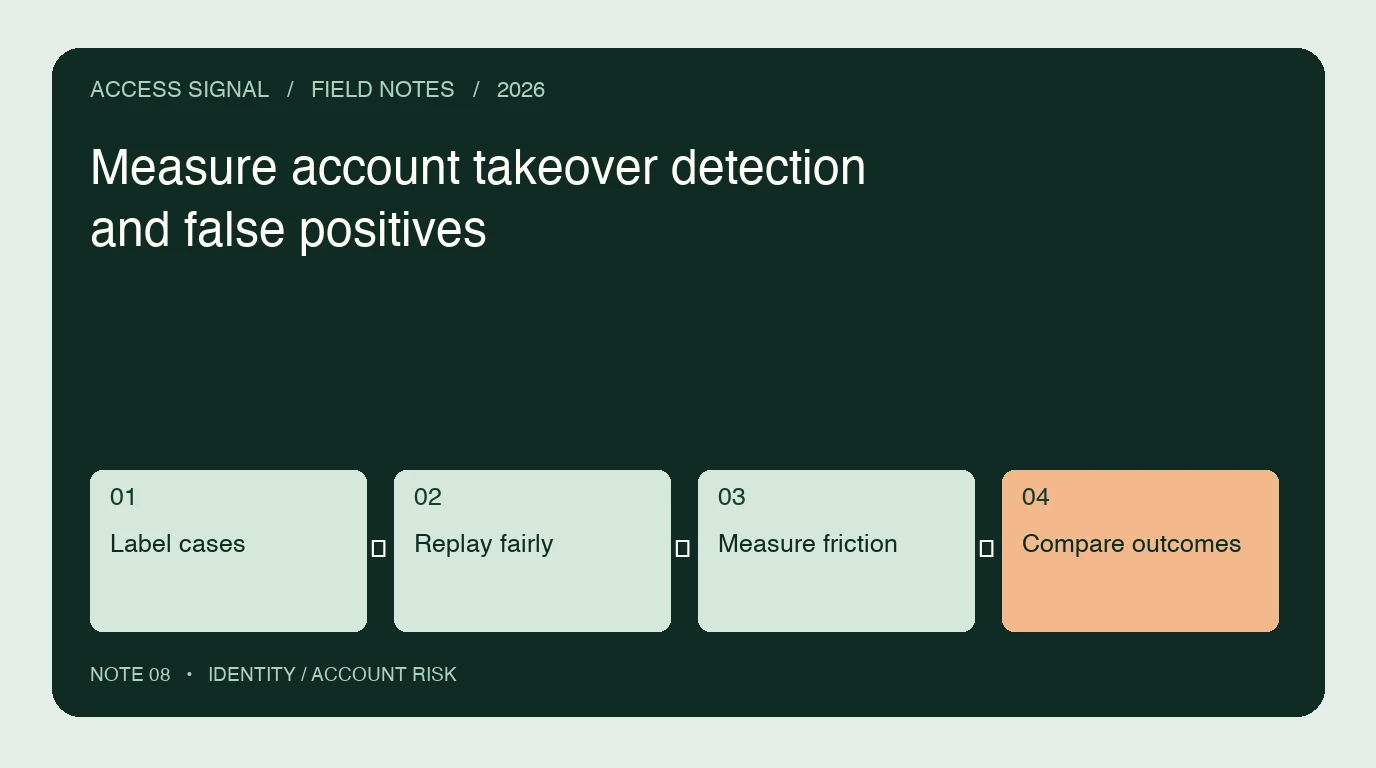
Measure account takeover detection and false positives
Evaluate ATO tools with confirmed outcomes, legitimate-owner friction, step-up completion, recovery results and explicit coverage and cost denominators.
Explore checkers, demos and evaluation routes →
Summarize this page with
Practical research guides
ATO software selection: detection, response and recovery
Compare account takeover software by access coverage, response integration, owner recovery, operating effort and transparent workload-based pricing requirements.
Device recognition in owner protection and visitor analytics
Interpret device familiarity, browser changes and visitor analytics without turning a match into account authentication, private access or verified identity.
ATO network, bot and credential defenses
Join distributed credential attempts, rotating exits, bot evidence and challenge handling to trusted login controls with a workable path for legitimate owners.
How to prevent account takeover across the access journey
Build an account takeover prevention plan across authentication, device and network risk, sensitive actions, session containment and protected recovery.
ATO, benefit misuse and partner account risk
Separate compromised access from trial, sharing, referral and partner-policy misuse, with explicit grants, qualification records and appropriate owner treatment.
ATO commerce loss: purchases, claims and specialist access
Retain account-access evidence through purchases, refunds, ticket transfers and support while preserving the responsibilities for each resulting loss event.