AUTHOR
Alexei Sorokin
Identity and Account Risk Editor at Access Signal. Authentication, current device/network evidence and account response shape his editorial coverage.
Editorial principle and publication standards
Product reviews
Practical guides
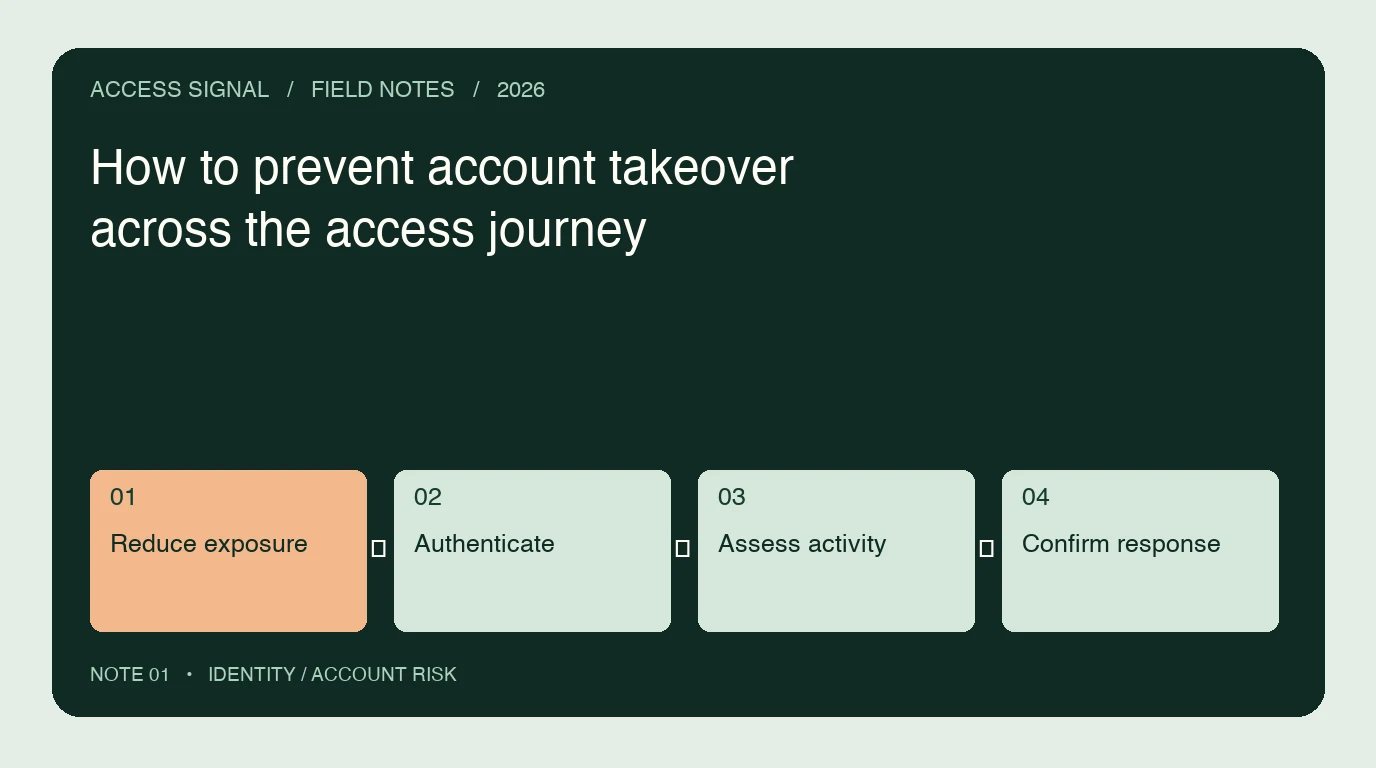
How to prevent account takeover across the access journey
Build an account takeover prevention plan across authentication, device and network risk, sensitive actions, session containment and protected recovery.
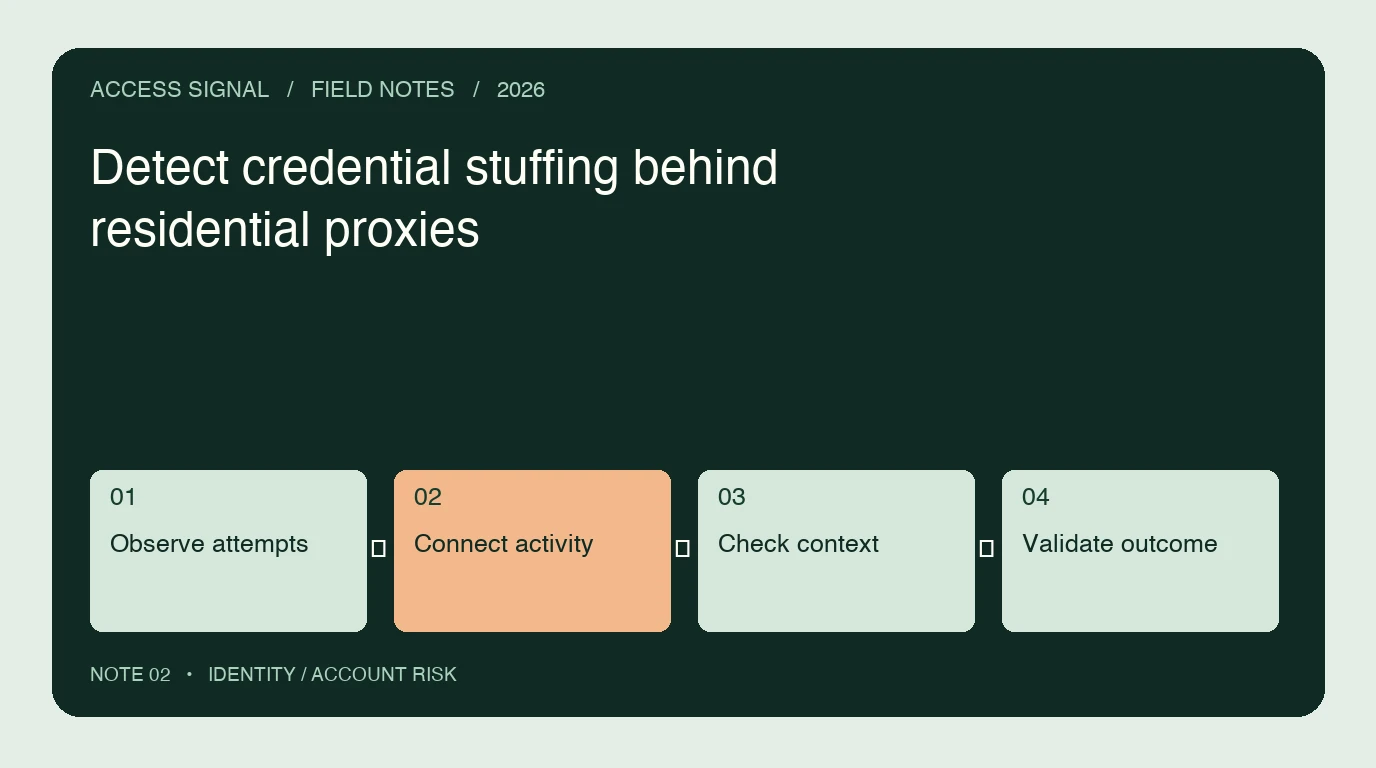
Detect credential stuffing behind residential proxies
Detect distributed credential stuffing with account, device and network evidence. Evaluate low-rate attempts, valid logins and legitimate shared-network users.
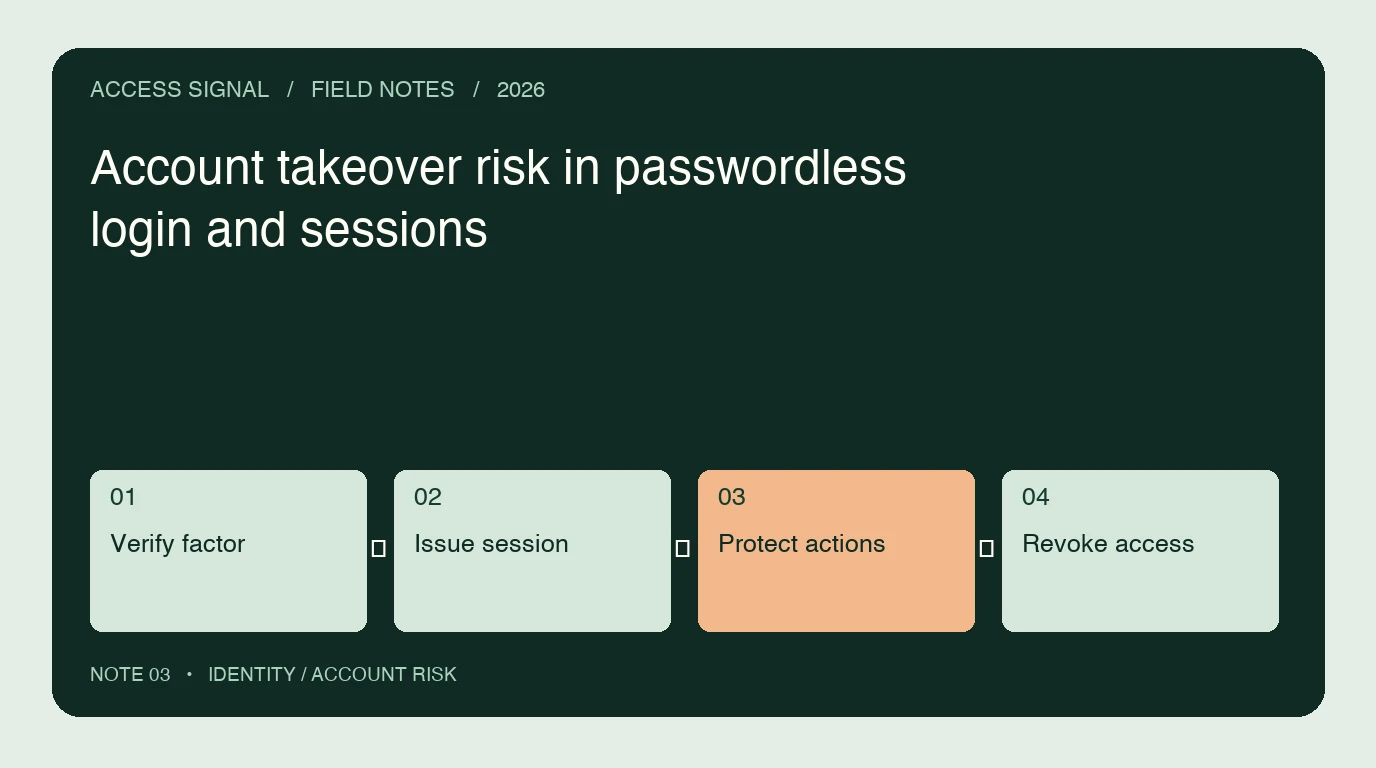
Account takeover risk in passwordless login and sessions
Understand what passkeys protect, where session and recovery risk remains, and how to evaluate account controls around a passwordless login journey.
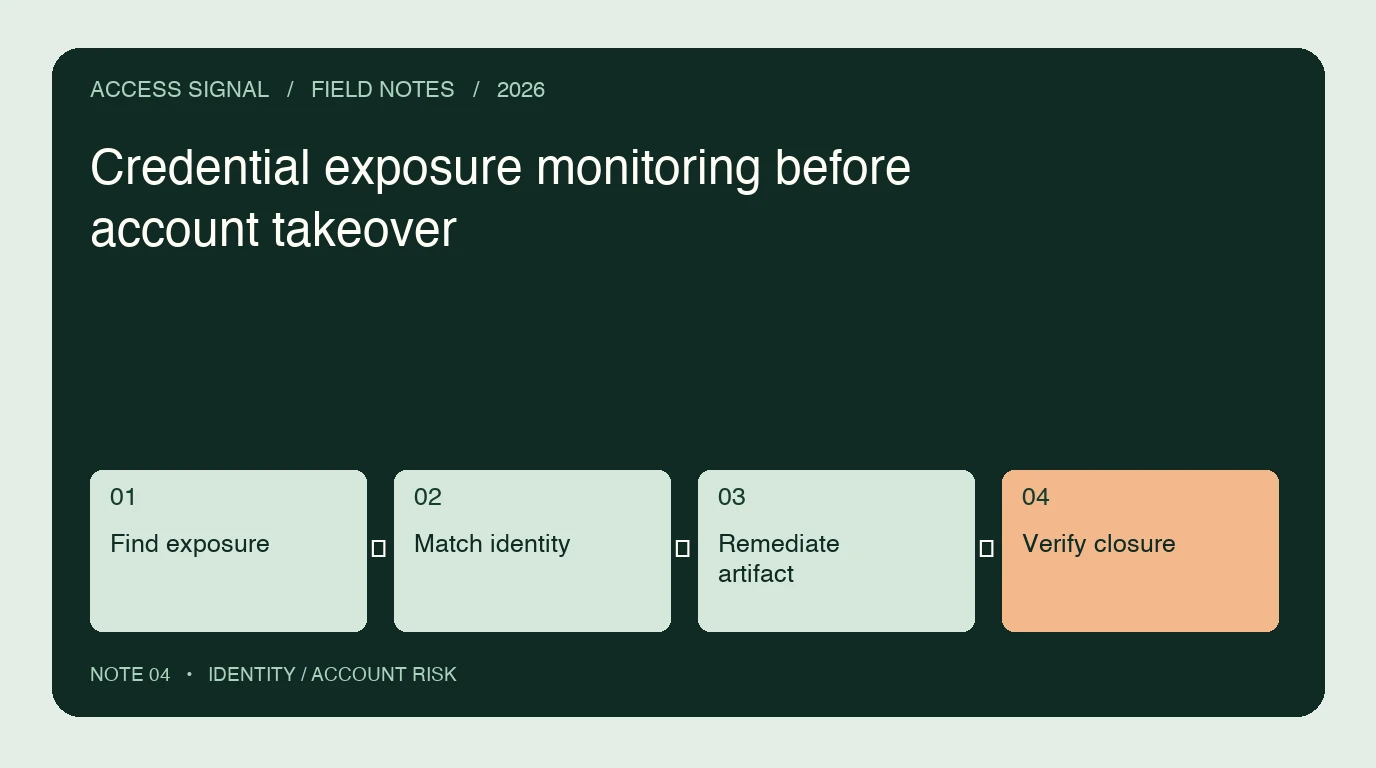
Credential exposure monitoring before account takeover
Compare compromised-credential and session-artifact monitoring with live login risk. Plan identity matching, remediation and verification without collecting raw secrets.
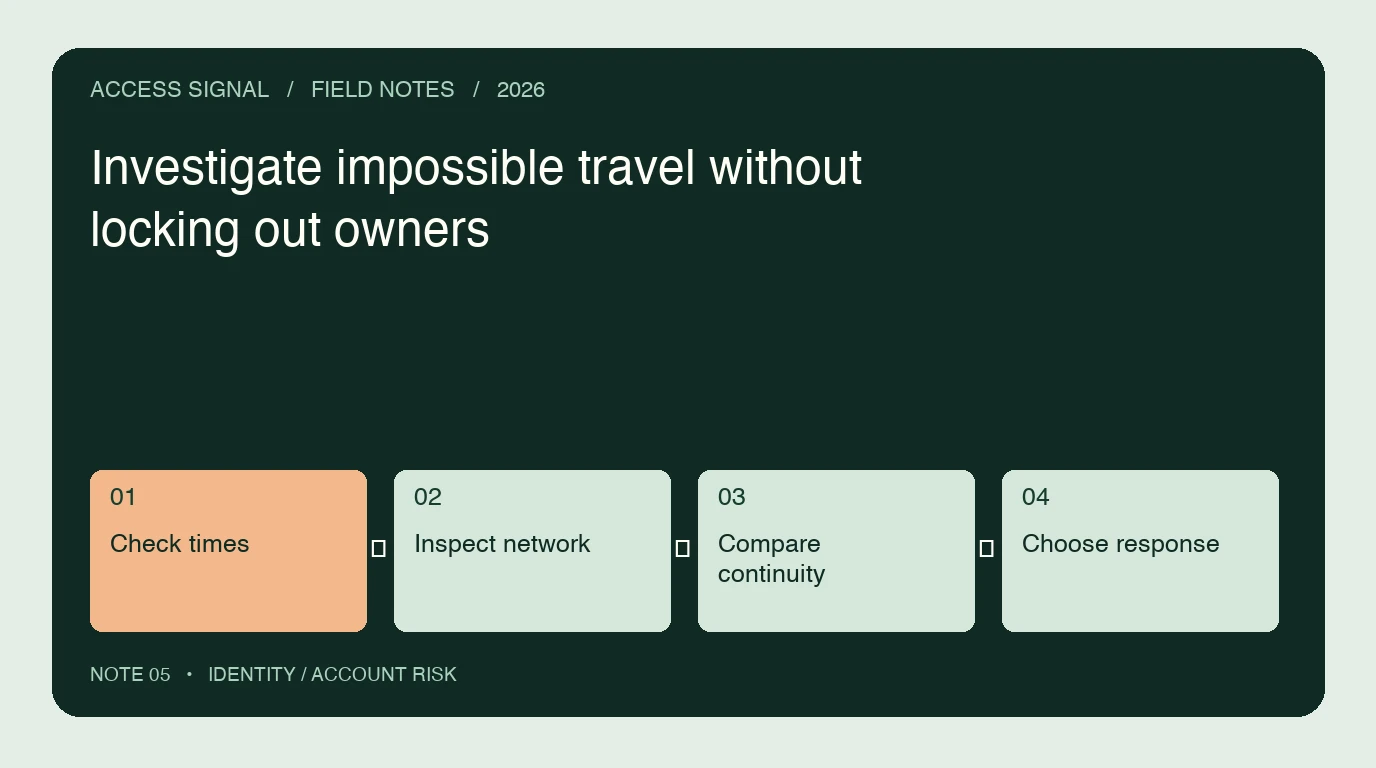
Investigate impossible travel without locking out owners
Investigate impossible-travel alerts with device continuity, network context, timestamps and session actions. Separate IP geolocation changes from confirmed compromise.
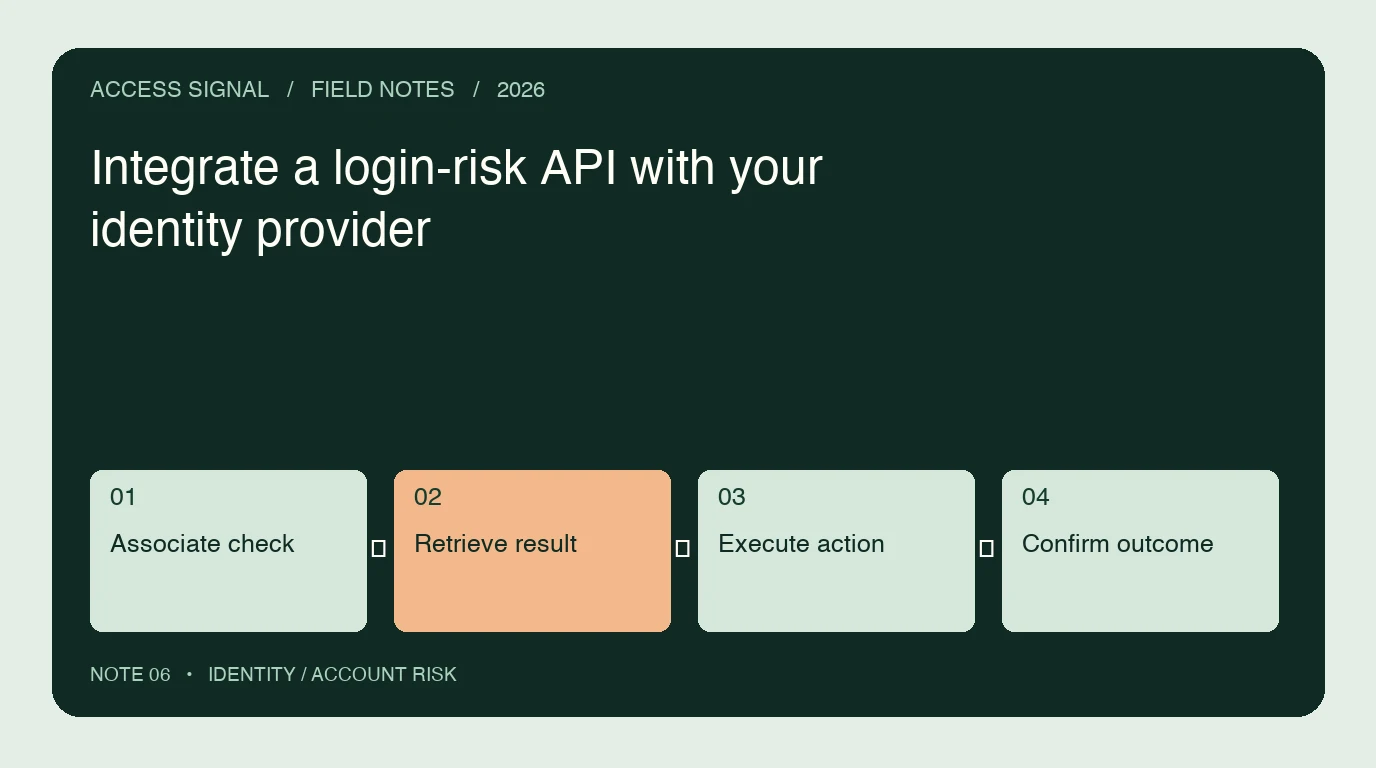
Integrate a login-risk API with your identity provider
Build trusted login-risk integration around account and action references, server-side results, freshness, step-up confirmation, timeouts and session controls.
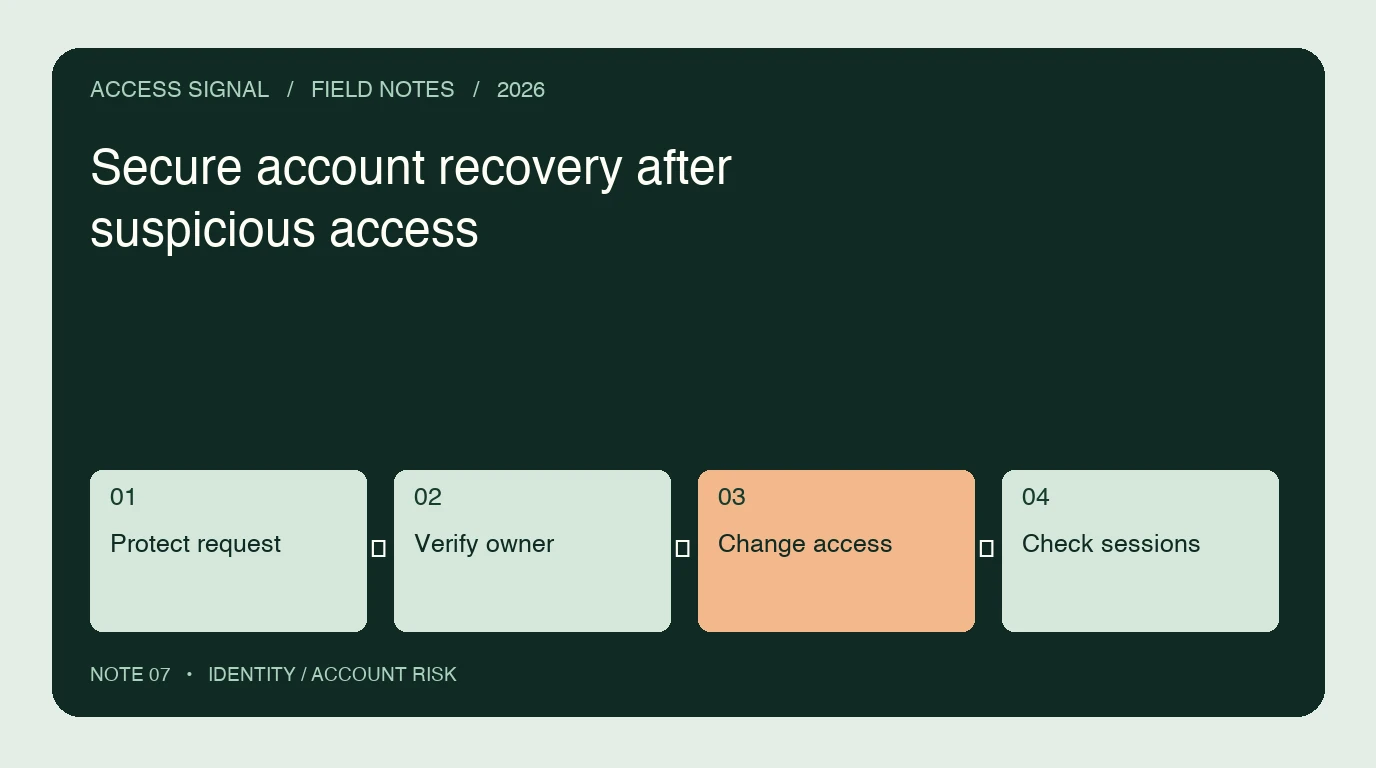
Secure account recovery after suspicious access
Protect account recovery with safe reset handling, proportionate device-risk checks, owner verification and confirmed session consequences after a reset.
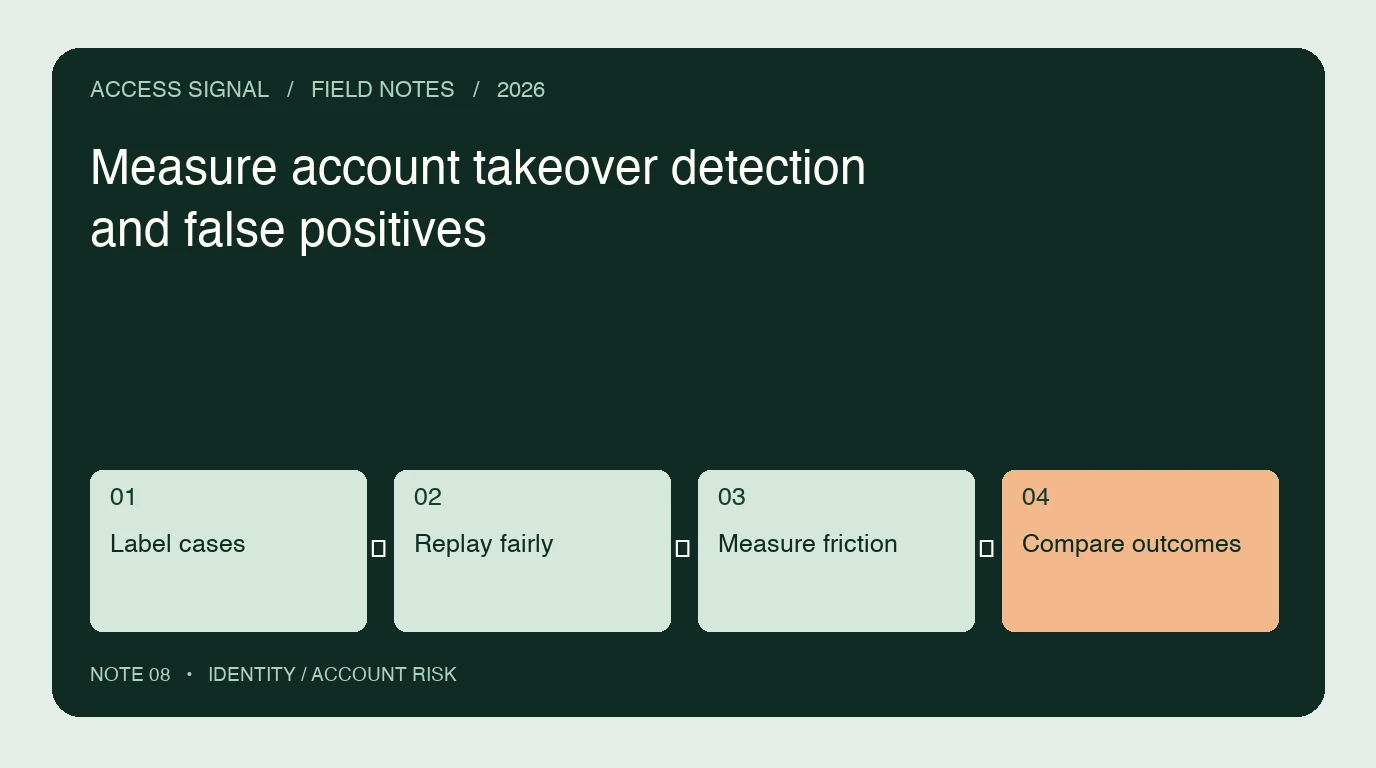
Measure account takeover detection and false positives
Evaluate ATO tools with confirmed outcomes, legitimate-owner friction, step-up completion, recovery results and explicit coverage and cost denominators.